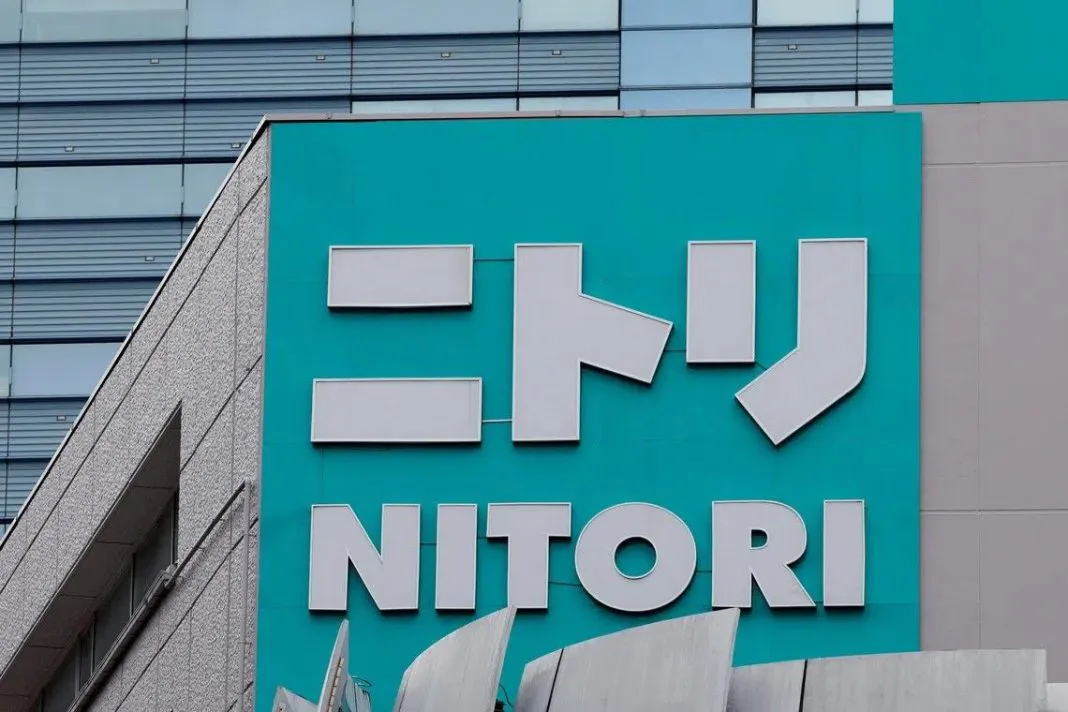
Up to 37.62 million customer records held by Japanese home furnishings retailer Nitori Holdings may have been leaked after unauthorised access to its systems, the company said on 9 Nov. The count covers members of the Nitori group and people who bought goods from the chain online, making it the latest Japanese company to report a possible data breach, according to The Star.
A notice from Nitori Holdings lists the data that may have left its servers: member numbers, names including their kana readings, email and postal addresses, telephone numbers, dates of birth and gender. Records for corporate members add company names, departments, the name of the representative and the contact person’s email and telephone number. Order data placed through Nitori Net and through the company’s official shops on e-commerce marketplaces is also in scope, and the combination of fields differs from customer to customer.
Login passwords and credit card information were not among the data that may have been exposed. Nitori confirmed the intrusion on 6 Nov, Mainichi said, and a third-party investigation placed the breach somewhere between mid and late October. The company said it has kept the attacker’s access blocked, addressed the vulnerable point and completed the strengthening of its monitoring.
Sega disclosed the same day that about 2.2 million customer email addresses had leaked after a contractor it uses to distribute newsletters was compromised. Names, telephone numbers, credit card information and login passwords were not included, BleepingComputer reported. The contractor, Arara, told Sega on 29 October that no data had been compromised before confirming the exposure on 3 November, and Arara has said the incident affected 77 million email addresses across nearly 380 corporate clients.
The 37.62 million figure counts records, not people, and Nitori has not said how many individuals are behind it. It has reported the matter to Japan’s Personal Information Protection Commission and is consulting police. The company has not said which system was breached, how the attackers got in, or whether it has received a ransom demand, and no group has publicly claimed the attack, CyberSixT noted.
Whether every record was accessed or removed is also still unconfirmed, per iSec News, and the total may change as log analysis and data matching continue. On what it currently knows, Nitori expects the impact on consolidated results to be limited.
Affected customers will be contacted by email or post. The retailer warned that the data could be used in impersonation emails, phishing and suspicious calls, including messages posing as Nitori, delivery companies or online marketplaces, and said it never asks for passwords, card numbers or PINs by email or telephone.
The investigation into the entry route and the full scope continues with external specialists.