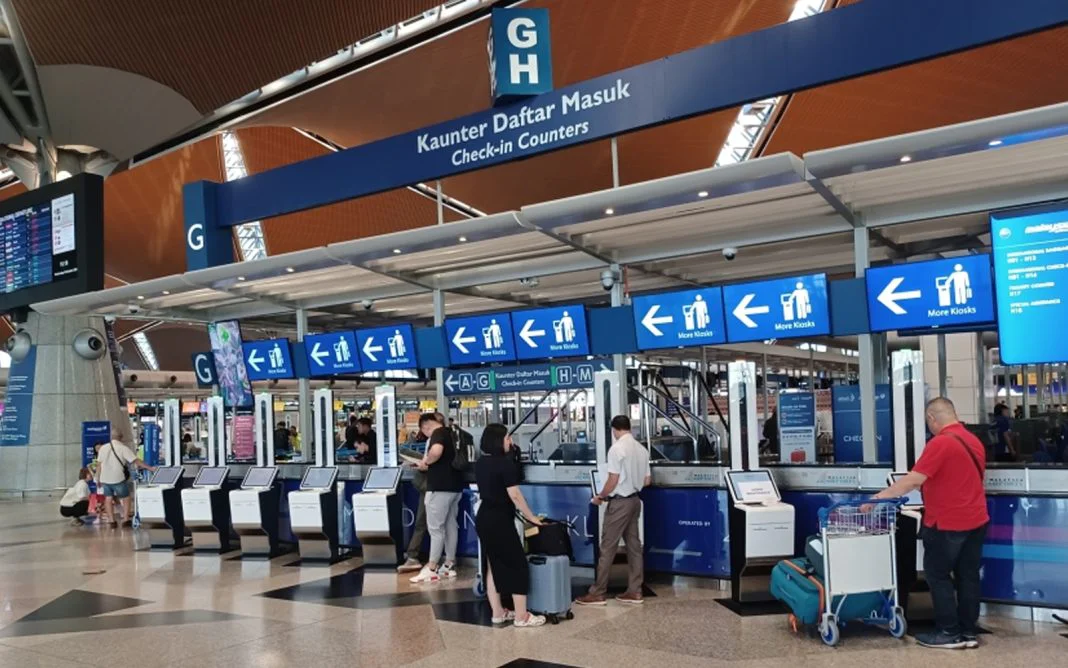
Malaysia Airlines Bhd said its own information technology systems have not been compromised, although a cybersecurity incident at Amadeus IT Group may have exposed customer details held by the Spain-based reservation provider.
The national carrier said information processed through Amadeus between August 2023 and September 2026 could have been affected, and that there is no evidence financial information was accessed. The exposure was disclosed in a statement on the airline’s website, which did not say how many customers were involved or which types of personal data may have been taken, NST reported.
Amadeus has since moved to close the gap. The travel technology company said certain booking-display data was accessible through a vulnerability, which it has now addressed, and that checks on the incident are continuing. “There are no indications that this vulnerability has been exploited for ransomware purposes,” it said in a statement.
Amadeus supplies reservation and other technology services to hundreds of airlines worldwide. Malaysia Airlines said it is working closely with the company and relevant parties to investigate the incident and assess its impact, a position also carried by The Star.
The breach reaches well beyond Malaysia. Cathay Pacific said on 30 October that about 53,000 of its bookings were affected by unauthorised access to passenger reservation data held by Amadeus. Most of the affected records held booking references, passenger names and flight details. A smaller number may also have included email addresses, phone numbers, travel document information and frequent flyer numbers.
The Hong Kong carrier said the unauthorised access involved login credentials assigned to an Amadeus system account, with affected records dating between August 2023 and September 2026. It was notified on 28 October and received further details the next day.
Japan Airlines and Japan Transocean Air reported that about 92,000 customers were affected, while All Nippon Airways said information relating to about 37,800 customers had been accessed. South Korea’s Korean Air and Asiana Airlines have also reported unauthorised access to customer reservation information through Amadeus, without disclosing numbers. Korean Air and Asiana were notified on 20 October, and the two Japanese carriers on 23 October.
Cathay Pacific said it found no evidence that financial or payment information had been accessed, and that its own systems and flight operations were unaffected. Amadeus said payment and financial data were not affected and that it has strengthened monitoring and detection on its systems.
Malaysia Airlines has advised customers to stay alert to suspicious or unsolicited messages, particularly those asking for personal or financial information. It said customer privacy remains its priority and that further updates will be provided as more information becomes available.
Amadeus said it is in direct communication with its customers and relevant authorities.